Important Notice from Linkedin
LinkedIn's User Agreement prohibits third-party software that automates activity on its website, and members who use such tools "risk having their accounts restricted or shut down."
GrowReach doesn't just get you leads, it gets you warm leads while keeping your account's safety as its 1st priority. By using your real browser session, human-like behavior, errors, and action well within the thresholds limits.
No automation is 100% risk-free anyone who tells you otherwise isn't being honest with you. Lets understand exactly how we reduce risk, and what we don't do.
Linkedin is not against automation, its against spam. If you post spam/low value content this is how Linkedin can limit you reach
LinkedIn's User Agreement prohibits third-party software that automates activity on its website, and members who use such tools "risk having their accounts restricted or shut down."
A temporary restriction (sometimes called "LinkedIn jail") specific features get limited for a while: sending connection requests, messaging, posting.
LinkedIn locks login and asks you to confirm you're a real person (email, phone, or government ID).
LinkedIn has enforced these rules at every level from individual accounts to vendors. It has removed company pages and restricted profiles of major automation vendors, and sued data-reselling companies out of existence.
The core issue isn't automation itself it's how a tool touches the platform. LinkedIn's detection systems analyze behavioral patterns at the session, IP, and account levels. Here's how GrowReach is built to stay on the right side of each one.
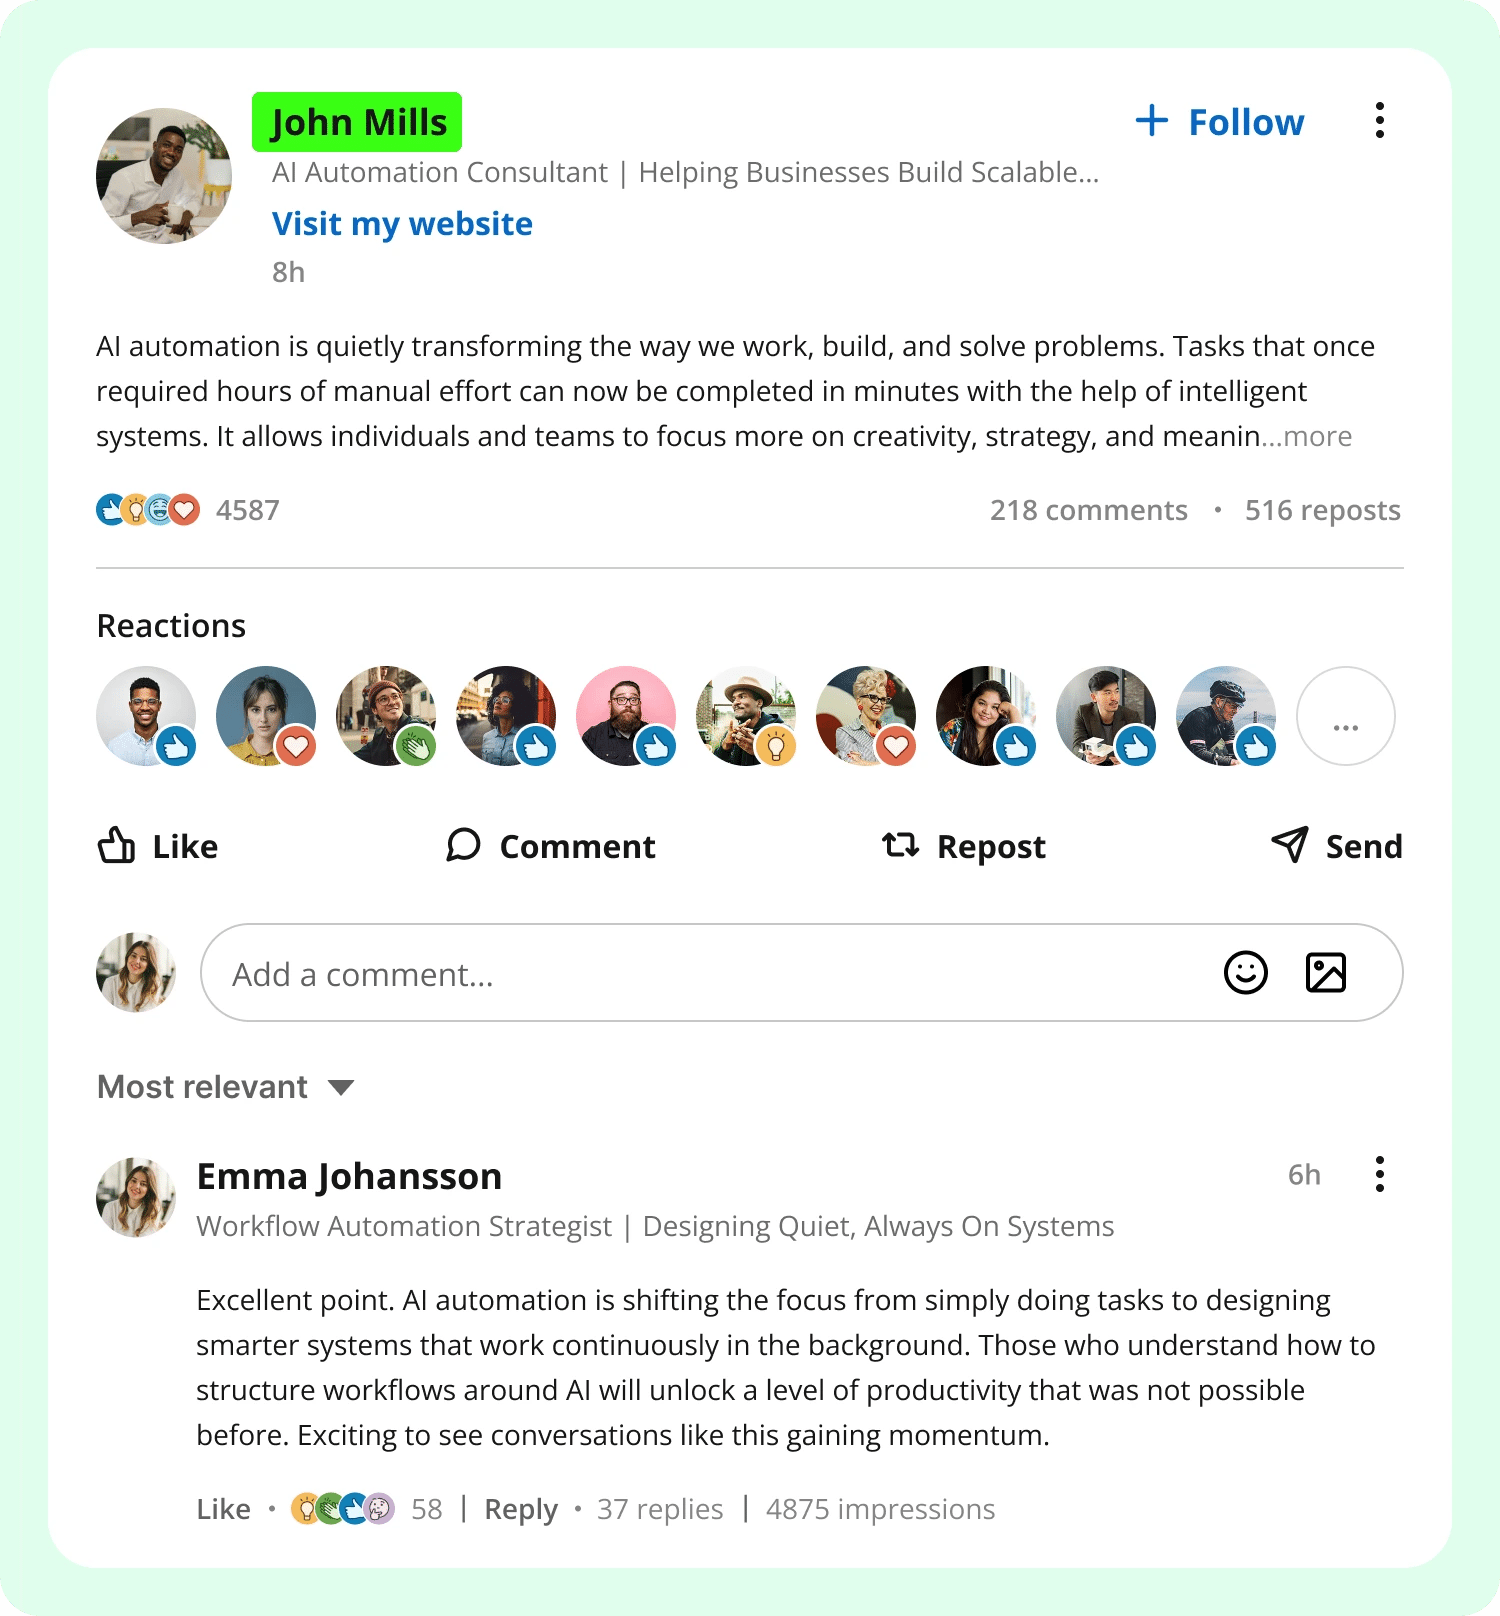
GrowReach works with your actual LinkedIn login, in a real browser the same way you use LinkedIn yourself.
Every action follows realistic pacing.
GrowReach does not rely on scraping APIs, mass automation servers, or shared automation fingerprints. This lowers detection risk compared to cloud-based tools. GrowReach Agent runs your browser session in the same IP location and within usual Linkedin usage hours to ensure Linkedin doesn't even get a chance to doubt your account
Automation always carries responsibility. GrowReach is built to support that responsibility, not avoid it.
We're not going to tell you automation is risk-free. It isn't, and anyone who says otherwise isn't being honest with you. There is no approved outreach automation tool ours included. Every tool in this space operates in the same reality. The only variable is how much detectable signal each one leaves.
Before you begin engaging, make sure your account and preferences are properly configured. GrowReach gives you a guided starting point, so you can build a thoughtful engagement workflow from day one.
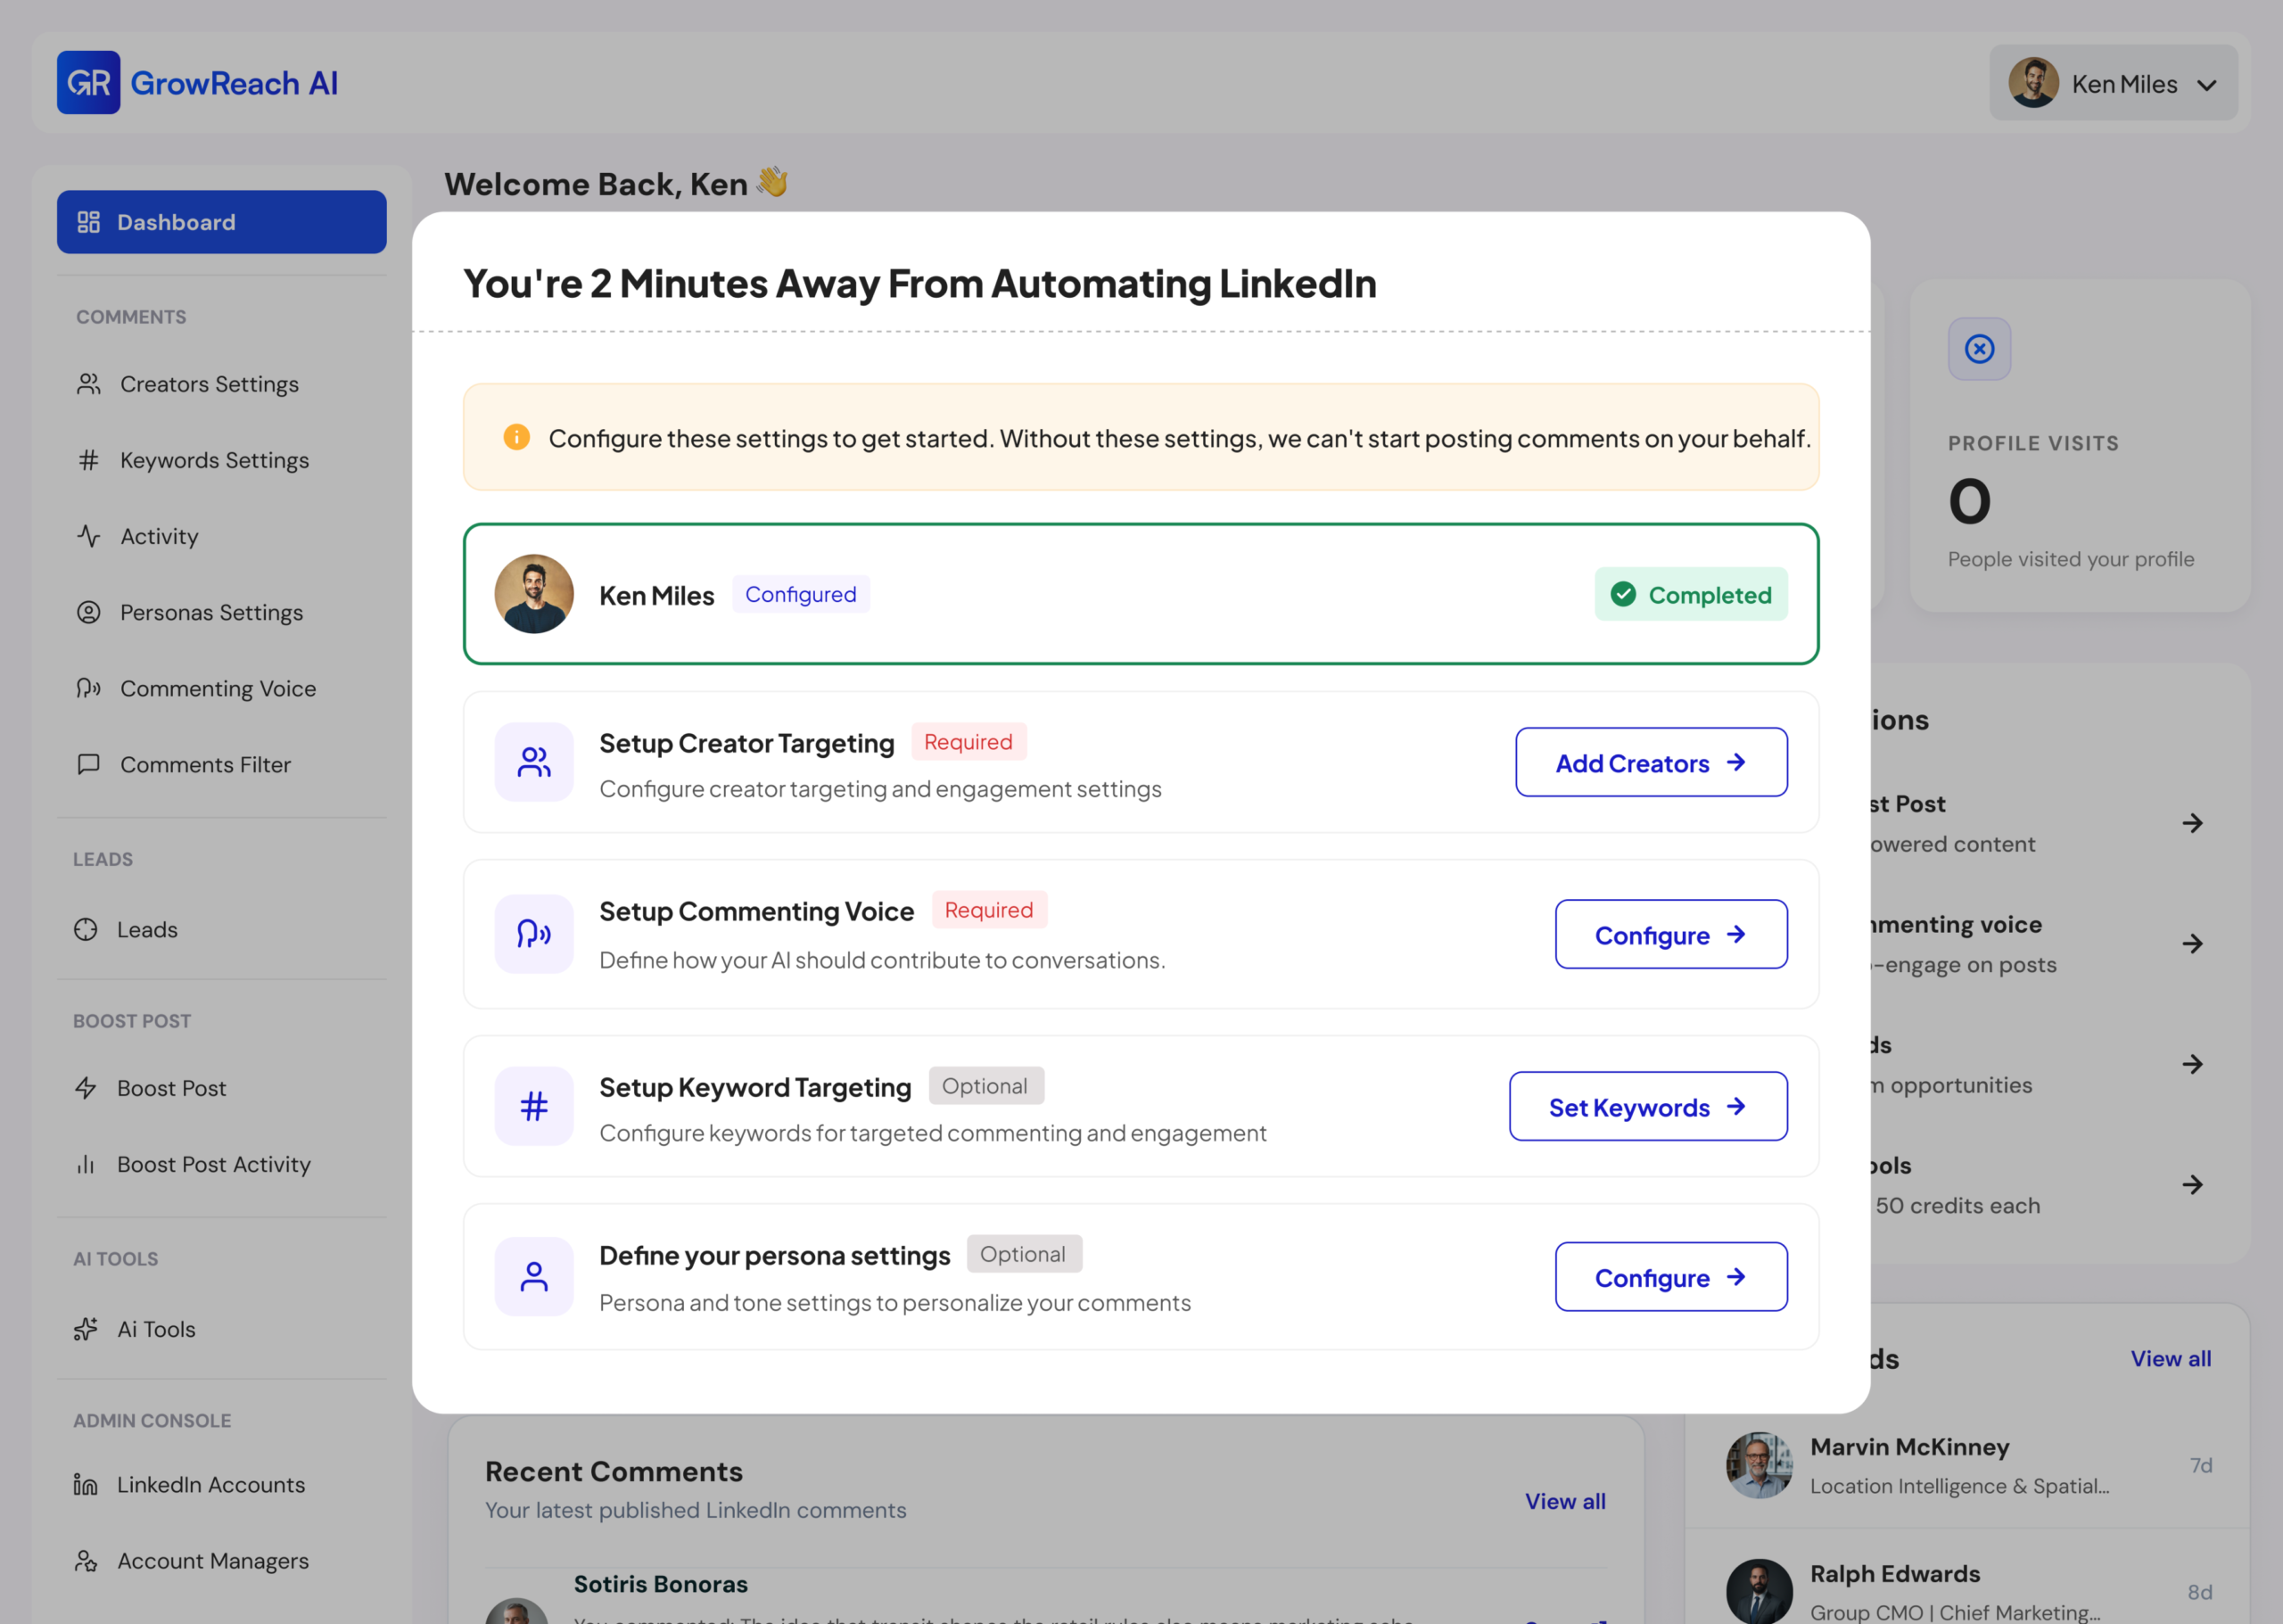

Set up your LinkedIn account and confirm that your connection is ready.

Choose relevant creators, people, and topics that align with your goals.

Configure how GrowReach should comment in your own style.

Complete the essential settings and take control of your engagement workflow.
It is not designed for spam, mass blasting, or policy abuse.

consistent, thoughtful commenting that makes you visible as an expert in the conversations that matter.

warm inbound leads from engagement, without the spammy patterns that get accounts flagged.

conservative by design, because a client's account is not something you gamble with.
GrowReach reduces risk by using your real session and human-like behavior, but no automation can be 100% risk-free. Restriction risk comes from behavior (volume, reports, IP anomalies), not from tools per se. A safe tool inside the limits is lower-risk than a human blasting 80 manual invites a day.
LinkedIn restricts accounts for detectable automation (browser extensions), excessive volume, and high "I don't know this person" report rates. The behaviors that trigger restrictions: browser extensions executing actions while LinkedIn is open; aggressive volume connection requests far above ~20–25/day, or unnatural spikes; high "I don't know this person" report rates the single most reliable spam signal LinkedIn has; IP inconsistency; data scraping without API authorization. GrowReach is built to avoid each of these patterns.
No. LinkedIn doesn't permit fake accounts or fake engagement, and neither do we. GrowReach works inside your real session, on your real account, generating comments in your voice.
Yes. Many agencies use GrowReach specifically because of its conservative, session-based design. But remember: you are responsible for anything that happens through your account.
No that's not our model. GrowReach works using your normal browser environment. Tools that require proxies or anti-detect browsers are usually hiding shared infrastructure the exact pattern LinkedIn's detection targets.
Human-like timing, conservative daily limits, and platform-aware rules built in, not optional. Safe-by-default beats safe-if-configured.
No, and we won't pretend there is. No automation can be 100% risk-free. What we can tell you: risk is an engineering problem, and we've engineered against every signal above. You are responsible for how you use GrowReach we recommend reading LinkedIn's User Agreement and using the product within its intended limits.
GrowReach is built for professionals who value account safety and long-term results.
Start 14-day free trialThis page is not legal advice. We're not lawyers and this isn't legal advice. LinkedIn revises these documents without much announcement, so if you're making a decision that matters, read the current version and get proper advice.
This page summarizes public policy and industry practice; it is not legal advice for your specific situation.
LinkedIn is a trademark of LinkedIn Corporation. GrowReach is an independent product and is not affiliated with, endorsed by, or sponsored by LinkedIn.
You are responsible for how you use GrowReach and for anything that happens through your account.